Hackers Are Raiding Retail for Customer and Staff Data, Study Finds
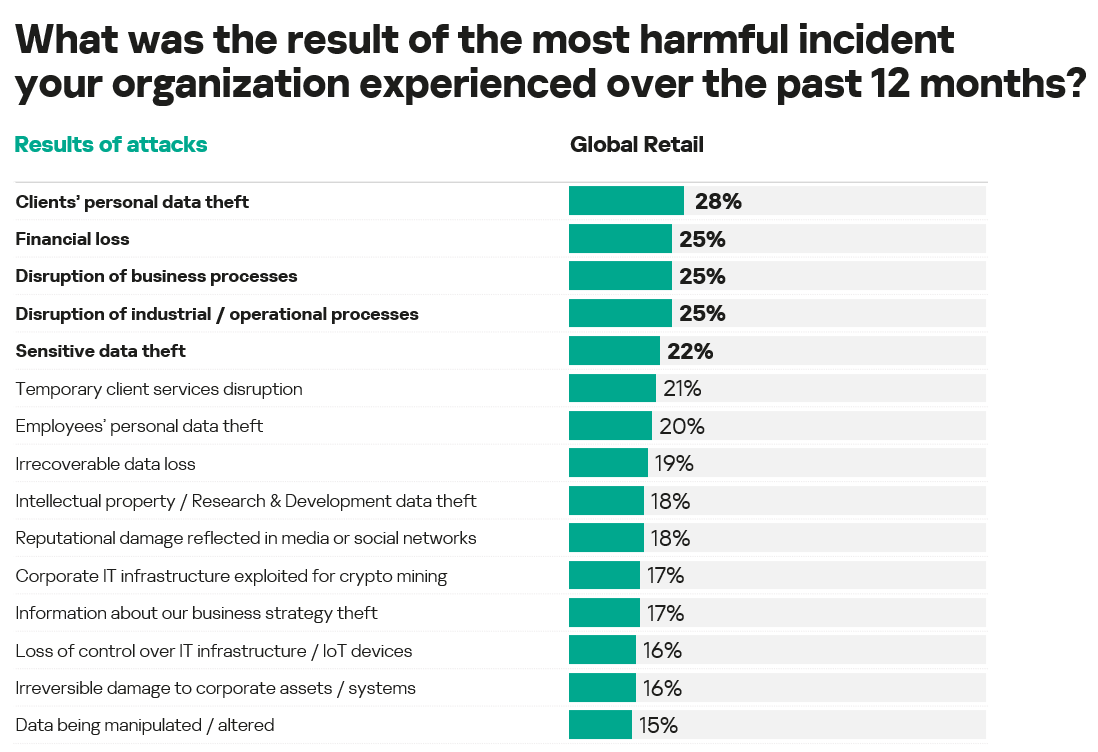
Retailers sit on a mountain of personal data, and cybercriminals know it. A Kaspersky survey found that 87% of retailers worldwide faced cyber incidents during the 12 months it covered, while only 13% escaped.
The global study, run by Kaspersky’s Internal Research Centre, surveyed IT security specialists in retail across 18 countries. Attackers’ primary aims were stealing clients’ personal data (34%) and employees’ personal data (28%).
Phishing and Deepfakes Lead Retail Cyberattack Threats
Retail spans everything from browsing to final payment, including e-commerce and loyalty programs. That reach piles up huge volumes of personal data, which makes the sector an attractive target for cybercriminals, according to Kaspersky.
Phishing was the most common threat, reported by 21% of retailers. Deepfakes and invoice or payment fraud each came in at 13%, followed by business email compromise (9%) and vishing, or voice phishing (8%).
Cyber espionage (19%) and web application exploits (18%) joined phishing among the three most frequently experienced incidents. Kaspersky said the mix shows retailers face manipulation of employees and partners, as well as complex attacks on online infrastructure.
APAC Retailers Report Employee and Customer Data Theft
In APAC, the most common results of attacks were theft of employees’ personal data (44%) and clients’ personal data (39%). Theft of sensitive data, such as financial credentials and legal documents, came in at 33%.
Irrecoverable data loss also reached 33%, putting business operations and sensitive information at risk. APAC respondents named a lack of IT security awareness (46%) as the top internal factor raising the likelihood of successful attacks.
Adrian Hia, Managing Director for APAC at Kaspersky, said the findings highlight a gap in retail cybersecurity in the region. He said protection must extend beyond the IT team and become part of how retailers operate and employees work.
Kaspersky recommends a continuous awareness program for all employees and clear AI usage policies that address inadvertent data exposure. It also advises keeping customer data, core applications and supply-chain workflows fully protected.